Governance bolted on at the end
Risk and compliance arrive after the architecture is set — serious findings mean costly redesign.
Governance as Code
Governance as Code isn’t something you buy. It’s something your pipeline proves.
Governance as Code is what you get when open projects are chained into one pipeline — from shared use-case prioritization to audit-ready evidence.
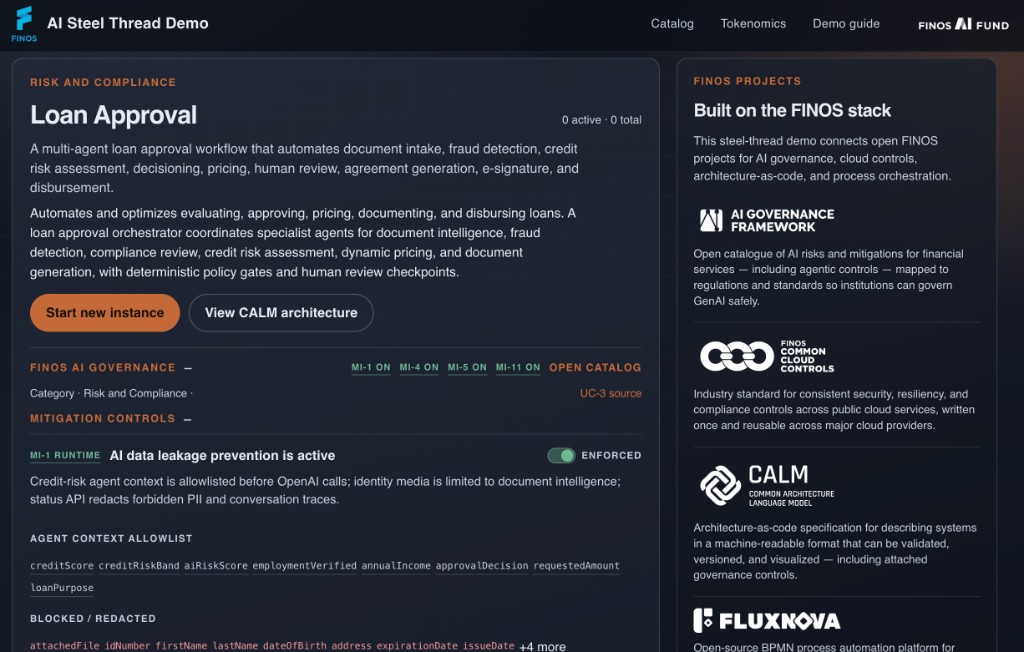
Practitioners will recognize these recurring patterns behind delayed launches, failed audits, and agents quietly pulled from production.
Risk and compliance arrive after the architecture is set — serious findings mean costly redesign.
Business units adopt agentic tools faster than central governance can track them.
When asked how a decision was reached, the answer is often “the model decided.”
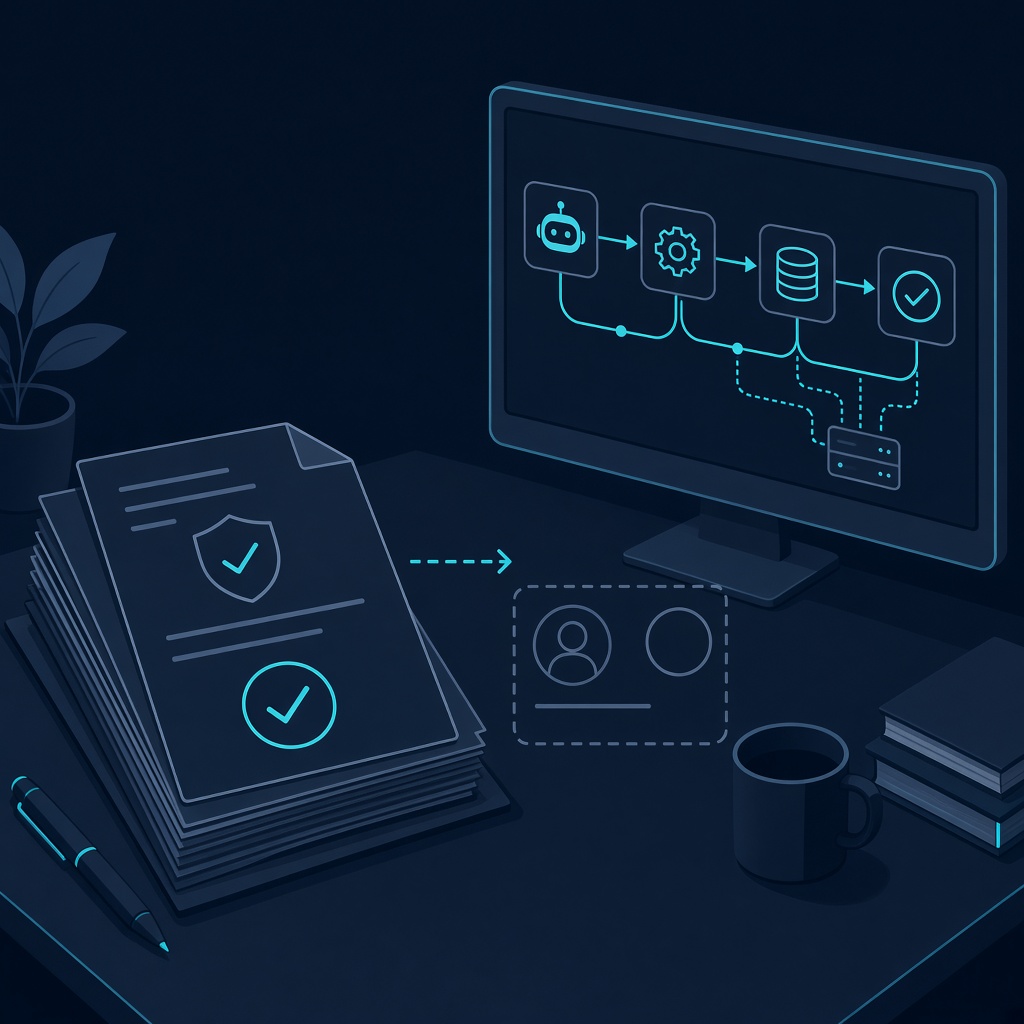
“Human in the loop” lives in policy documents but nowhere in the running system.
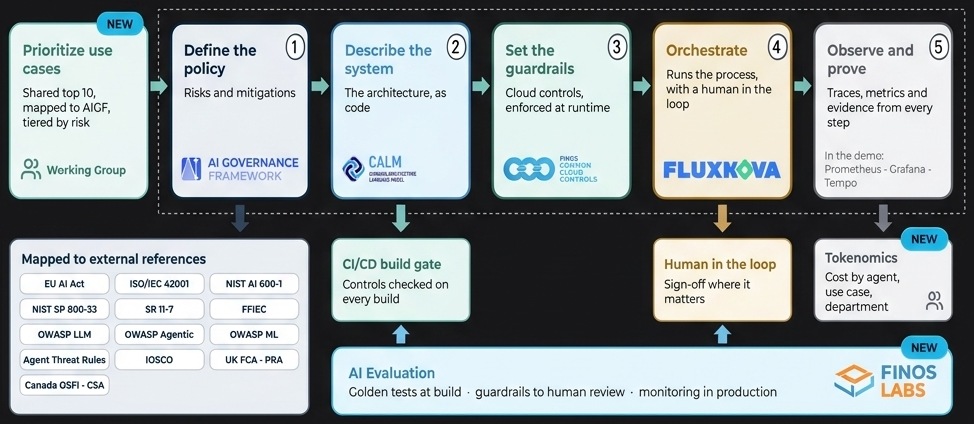
One open pipeline from use case to evidence. Each card links to the stage section below. Built in along the way: a CI/CD build gate that checks controls on every build, and human sign-off where it matters.
From a catalog of potential use cases — prioritization by the Use Cases Working Group, mapped to AIGF and tiered by risk.
 1
Risks and mitigations, in the AI Governance Framework (AIGF).
 2
The architecture, as code, in CALM.
 3
Cloud controls enforced at runtime, with Common Cloud Controls (CCC).
 4
Fluxnova runs the process, with a human in the loop.
Traces, metrics and evidence from every step (Prometheus, Grafana and Tempo in the demo).
Controls checked on every build before anything ships.
Sign-off where it matters — enforced in the process, not only in policy.
Pipeline start
A catalog of potential use cases — prioritization is the result of the Use Cases Working Group, mapped to AIGF and tiered by risk. Start from a common taxonomy so institutions compare and govern use cases consistently — whether fraud detection, autonomous trading, or AI-aided software development.
Draw from a shared catalog of potential pre-competitive use cases, then prioritize — mapped to AIGF risks and mitigations — so funding and delivery focus where governance matters most.
Classify systems across dimensions like AI type, architecture pattern, and data handling requirements so risk and controls scale to what a system actually does.
Explore the Taxonomy →1 — Define the policy
Risks and mitigations, in the AI Governance Framework (AIGF). AIGF is the foundation of the pipeline — defining what to govern so architecture, controls, and orchestration share one industry baseline.
A standardized catalog of governance controls for AI and agentic systems — covering model selection, autonomy levels, operational oversight, supply chain integrity, and regulatory alignment.
Explore the Catalog →2 — Describe the system
The architecture, as code, in CALM — plus reference patterns for FSI AI systems.
Transforms governance policies into machine-readable, executable specifications so institutions can embed compliance checks in CI/CD, development workflows, and runtime environments.
Learn more →FSI-specific AI reference architectures and threat models that consider AIGF catalog risks — including patterns for multi-agent and tool-using systems.
Explore Library →Controls checked on every build. CALM CI/CD integration validates agents and orchestration logic against AIGF-defined policy before anything ships.
3 — Set the guardrails
Cloud controls, enforced at runtime, with Common Cloud Controls (CCC).
Standardized cloud security and compliance controls for AI workloads — mapping regulatory expectations to actionable technical controls for hybrid and multi-cloud environments.
Learn more →4 — Orchestrate
Fluxnova runs the process, with a human in the loop — sign-off where it matters.
BPMN/DMN orchestration that defines deterministic process boundaries around non-deterministic agent behavior — with full execution tracing for audit.
Human oversight is enforced in the running process — gateways and decision rules that require sign-off — not only asserted in a policy document.
Learn more →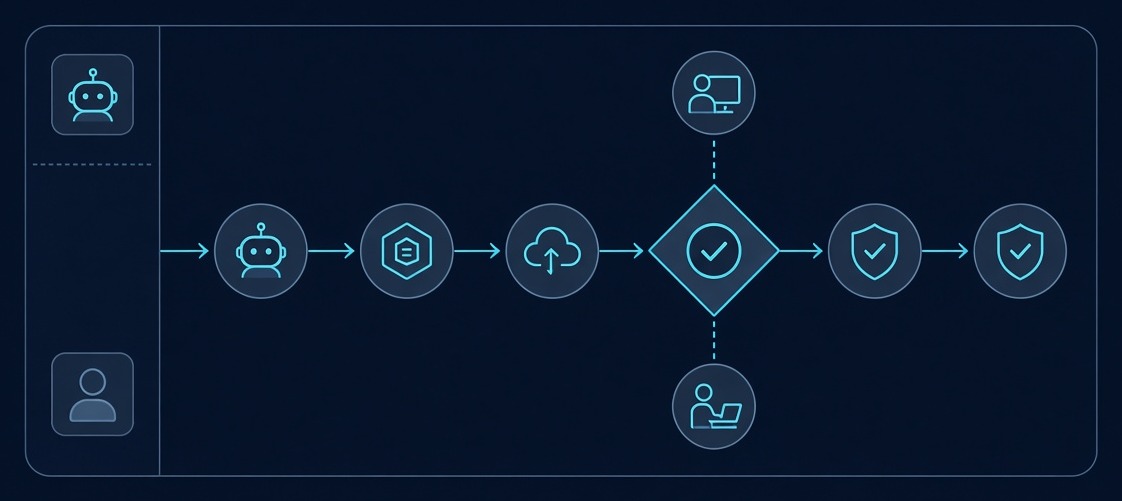
5 — Observe and prove
Traces, metrics and evidence from every step. In the Steel Thread Demo that means Prometheus, Grafana and Tempo — so an institution can reconstruct how a decision was reached.
Open instrumentation capturing real-time traces, metrics, and logs from running agents and orchestration.
Dashboards and traces that turn runtime behavior into operational and compliance signal — the evidence layer of the pipeline.
Two capabilities that cut across the pipeline — both marked new for the OSFF New York message.
Golden tests at build, guardrails that route to human review, and monitoring in production. A FINOS Labs project.
Cost by agent, use case and department — attribution across the governed workflow.
Go deeper with the Playbook, see the pipeline run, join the Use Cases Working Group, contribute controls, or get leaders trained on AIGF.
First Edition — Draft. A practical guide through the Governance-as-Code pipeline, worked against a KYC use case.
Open the Playbook →Download PDF →The AI Steel Thread Demo — the pipeline end to end, powered by the FINOS AI Fund.
Run the demo →Help grow the catalog, prioritize use cases mapped to AIGF, and contribute taxonomy entries.
Get Involved →Improve the framework and the Playbook — open text a regulator or peer institution can reuse.
AIGF on GitHub →Playbook on GitHub →